
Bitcoin first appeared publicly as an eight-page PDF and an unknown name, not as a running network. That message landed:
Satoshi Nakamoto (Cryptography mailing list post, October 31, 2008, 6:10:00 PM UTC)I’ve been working on a new electronic cash system that’s fully peer-to-peer, with no trusted third party.
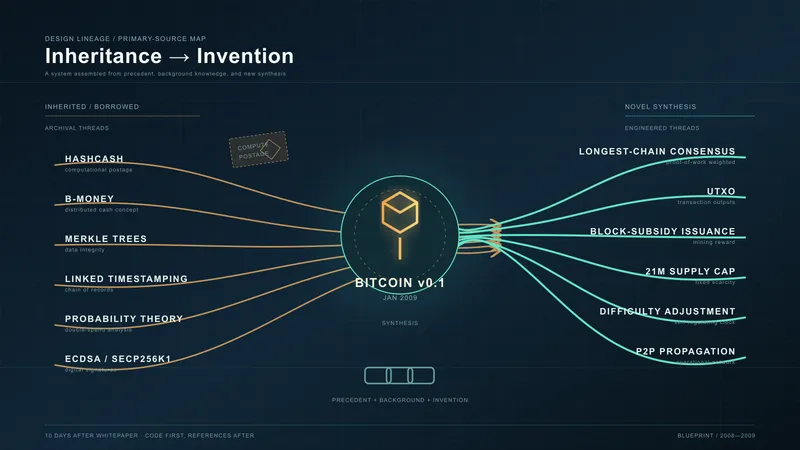
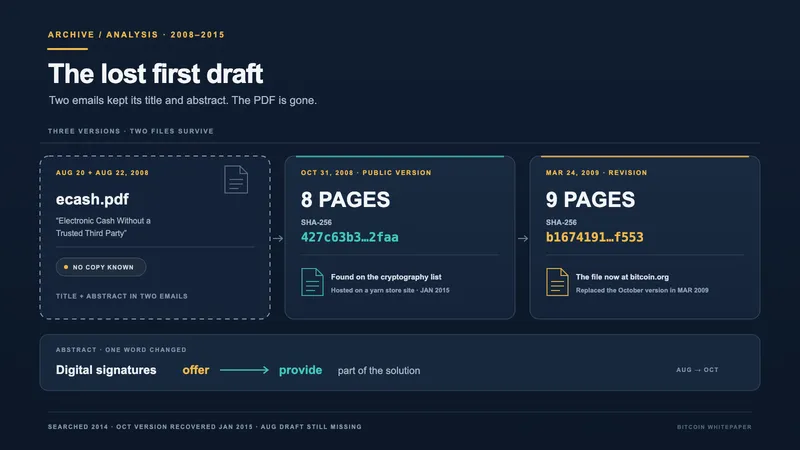
The name at the bottom was Satoshi Nakamoto. The message linked an eight-page PDF hosted at bitcoin.org, titled Bitcoin: A Peer-to-Peer Electronic Cash System, and listed five properties: double-spending prevented by a peer-to-peer network, no mint or trusted parties, anonymous participants, new coins issued through Hashcash-style proof-of-work, and that same proof-of-work powering the network that prevents the double-spending. The paper as posted is archived here, alongside the nine-page revision of March 24, 2009 that later replaced it at the same address.
It arrived amid a run of posts on hash functions. On October 29 the list had carried the announcement of Skein, a candidate in NIST’s competition to replace the SHA family, and a repost of Bruce Schneier’s blog post about it, and that thread was still going on the morning of the 31st. The next message after Satoshi’s, at 17:33 EDT, was Ray Dillinger’s on side-channel attacks.
Then, for two days, nothing.
The first reply in the record opened with a need and closed with a doubt:
James A. Donald (Cryptography mailing list post, November 02, 2008, 11:46:23 PM UTC)We very, very much need such a system, but the way I understand your proposal, it does not seem to scale to the required size.
James A. Donald, a longtime cypherpunk, had named in the thread’s first response the objection that would follow Bitcoin for the rest of its documented history: scale — first-responder standing that later made him a named Satoshi-identity candidate in his own right. The fuller reception history follows the same first replies through the years that came after.
John Levine answered from the anti-spam trenches, where the arithmetic looked hopeless — the blacklist operators he knew logged on the order of a million new hijacked machines a day, so the assumption that honest nodes would hold the most CPU power struck him as already refuted. The list Satoshi had chosen was the one audience for which none of this was abstract: its readers had built, reviewed, or buried a generation of digital-cash designs.
The register shifted. Hal Finney — the one reader who had himself built and shipped a proof-of-work token system, RPOW — replied:
Hal Finney (Cryptography mailing list post, November 07, 2008, 11:40:12 PM UTC)Bitcoin seems to be a very promising idea.
Finney connected the design to Nick Szabo’s bit gold and pressed on the well-funded-attacker problem. Satoshi answered point by point over the following two days, working through follow-up questions on block propagation, competing chains, and Finney’s request for concrete data structures, until one reply, fixed the project’s chronology in a single disclosure:
Satoshi Nakamoto (Cryptography mailing list post, November 09, 2008, 1:58:48 AM UTC)I actually did this kind of backwards. I had to write all the code before I could convince myself that I could solve every problem, then I wrote the paper.
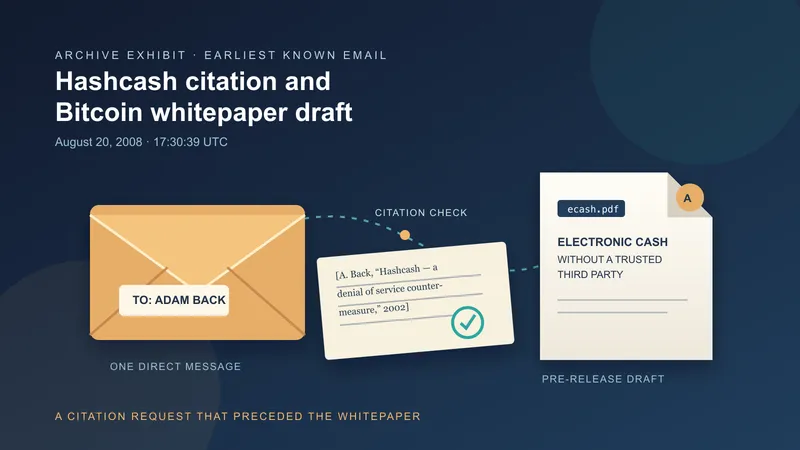
The eight pages were a report, not a proposal. Satoshi first wrote the code, confirmed against a working implementation that every problem could be solved, and then wrote the paper — so by the time the list read the abstract, the system it described already existed as software awaiting release. The paper had also moved privately before it moved publicly: in August, Satoshi wrote to each of the two cypherpunk predecessors it cited, asking Adam Back and Wei Dai about citing their work. The draft he linked in those emails has never resurfaced.
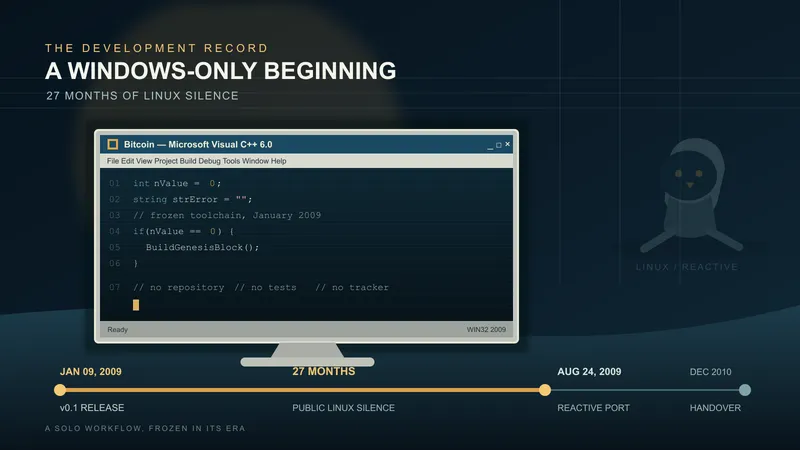
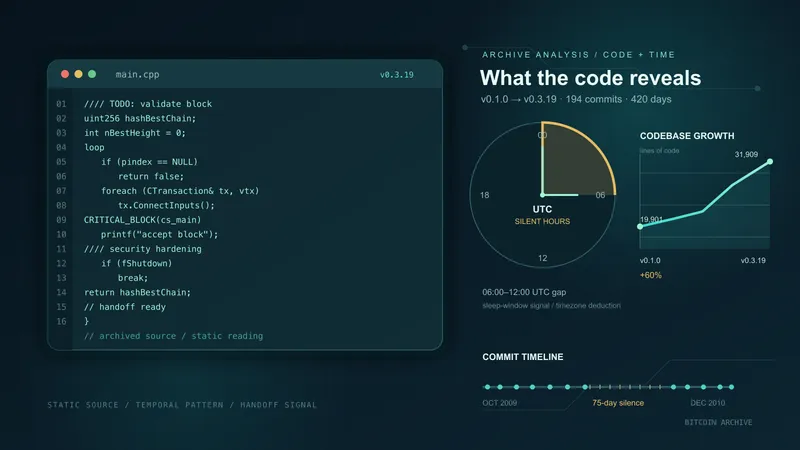
On November 17, replying to Donald, Satoshi located the code in time: “I believe I’ve worked through all those little details over the last year and a half while coding it, and there were a lot of them.” Two months later, that code shipped as v0.1.0 at 19,901 lines — a size the thread’s own back-and-forth over inventory broadcast and block propagation may well have helped shape in the interval.
Satoshi would later describe the same pre-release work at a wider scope, telling Mike Hearn in 2011 that “this project was 2 years of development before release” — the retrospective figure folding in the months spent thinking through the problem before any code existed at all, as this archive’s fuller reading of Satoshi’s Windows development environment traces in detail. Then the list’s moderator, Perry Metzger, called an end to the discussion on November 17, with the skeptics unconverted. Every message this archive holds from it — every objection, every answer — can be read in sequence in the thread view. Nine weeks after the announcement, Satoshi mined the genesis block, and the system the eight pages described stopped being a document.
What the list read as an untested proposal was, by the time they read it, already a settled fact of code. The two days of silence and the scaling objection that followed were never a verdict on whether the idea could work — Satoshi had already spent a year and a half finding that out alone. They were the sound of a skeptical audience catching up to a decision that had already been made.